
One Platform.
Every Wavelength.
Pryzma turns the records a regulated industry runs on into intelligence a small team can act on. It ingests the data, traces every figure to its source and runs agents that watch it continuously, so one person does what used to take a department.
One platform. Built out for each industry.
Pryzma sits between an organization's records and the decisions that matter: it ingests the data, traces every figure to its source, and runs agents that watch it continuously. Each industry gets applications made for its own records and regulators, on that same core.
Healthcare
Behavioral health providers, health information exchanges and state agencies
Privacy monitoring across a statewide health information exchange, behavioral health reporting to state agencies, and the analytics that run a clinic, all from the EHR and HIE data an organization already has.
- 11M+
- patient access events monitored
- 200+
- organizations in a statewide HIE network
- 21
- states served
- HIPAA and HITECH
- State behavioral health reporting
- SAMHSA CCBHC quality measures
Compliance Intelligence
Privacy surveillance for HIPAA. Anomaly detection, intelligence briefings, forensic investigations and thresholds that adapt to every confirmed or dismissed alert.
Learn more →
State Reporting
Behavioral health reporting to multiple state agencies. Database-driven validation, EHR integration and the full submission lifecycle.
Learn more →
Analytics & Insights
Operational intelligence across an HIE. Patient attribution, care pathway mapping, workgroup benchmarking and live dashboards.
Learn more →
CCBHC Reporting
SAMHSA quality measures for Certified Community Behavioral Health Clinics, tracked as they happen, with gap detection and submission-ready workbooks.
Learn more →
KPI Dashboard
Performance across seven domains: revenue cycle, clinical operations, workforce, credentialing, community, finance and program caseloads. Calculated from the EHR nightly.
Learn more →
Prior Authorization
Prior authorization review with confidence-scored recommendations, queue routing, auto-approval for routine cases and turnaround tracking.
Learn more →
Mining & Critical Minerals
Copper and critical-mineral producers and explorers
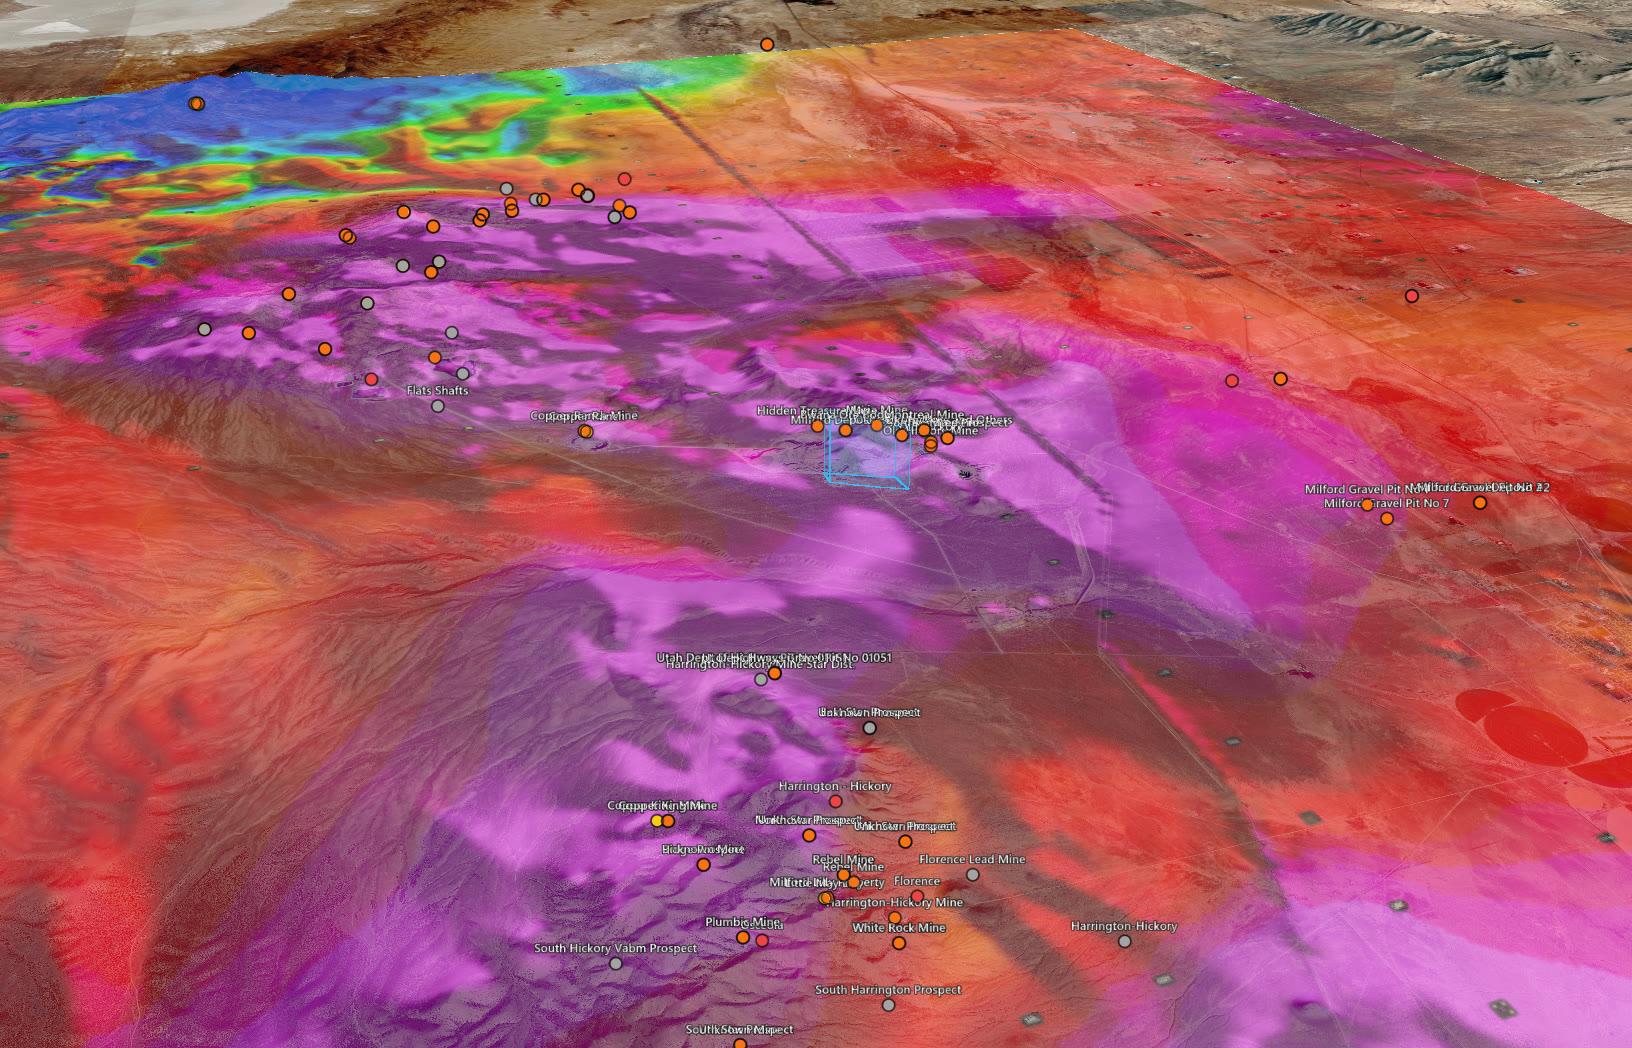
A century of surveys, technical reports, drill holes and public geophysics for a district in one 3D model, searchable to the page and reconciled across coordinate systems. CUI-capable and deployable to AWS GovCloud (US).
- 312
- sources catalogued for one district
- 3,936
- pages searchable, cited by page
- 870
- historical workings placed in 3D
- Every figure cited to its source page
- CUI controls (NIST SP 800-171)
- AWS GovCloud (US) deployment
Intelligence That Learns
Pryzma doesn't just run queries — it investigates. Built on a proprietary intelligence architecture with purpose-built domain reasoning, the platform generates hypotheses, tests them against your data, and learns from every investigation outcome. The result is a system that gets sharper the longer it runs — not a chatbot that gives you the same answer twice.
Ingest
Connect an EHR or HIE feed, a records archive or a data pipeline. Pryzma normalizes HL7 messages, FHIR resources, access logs, scanned reports and spatial data into one governed layer. No manual mapping. No middleware. Data flows in structured, governed, and audit-ready from day one.
Analyze
Proprietary AI agents watch the data continuously, flag anomalies with adaptive sigma-based detection and surface intelligence briefings, not just alerts. In healthcare, threat classification runs on a 5-tier model trained on de-identified healthcare access patterns, not generic anomaly detection borrowed from another industry.
Act
Investigate with conversational AI. Confirm, dismiss, or escalate findings — and the system learns from every outcome, sharpening future detection. Every action feeds back into the reasoning engine. Every investigation makes the next one faster.
Built Different. On Purpose.
Most AI platforms are wrappers around someone else's model with a logo on top. Pryzma is a vertically integrated intelligence architecture, hardened for the regulated environments where our customers operate: HIPAA in healthcare, CUI and AWS GovCloud (US) where a federal contract requires it.
Proprietary Reasoning Engine
Pryzma's core intelligence is built on domain-native reasoning, not a general-purpose language model fine-tuned after the fact. In healthcare, its models are trained on de-identified data under HIPAA Safe Harbor standards and read clinical workflows, access patterns and compliance signals natively. In mining, it reads survey plates, technical reports and drill logs and keeps every figure tied to the page it came from.
Adaptive Threat Classification
Our 5-tier threat classification system doesn't rely on static rules. It learns from your investigators' decisions — confirmations, dismissals, escalations — and continuously recalibrates detection thresholds to your organization's risk profile. The model that watches your data today is better than the one that started, and tomorrow's will be better than today's.
Foundation Model Integration
Pryzma's architecture integrates leading foundation models — including Anthropic's Claude — for conversational investigation, natural language querying, and report generation. But the intelligence is ours. The foundation model provides language. Pryzma provides judgment. Your data never trains third-party models. Regulated data, PHI or CUI, never leaves the governed pipeline.
Compliance by Architecture
Security and compliance aren't features bolted on after launch. Pryzma's data pipeline is governed end to end: BAA coverage at every layer for healthcare, CUI controls for federal work, AES-256 encryption in transit and at rest, role-based access controls, full audit logging, and data residency controls. We can show you exactly where your data goes, what touches it, and what doesn't.
The Questions Your CISO Will Ask
When your security team evaluates an AI platform, they're going to ask hard questions. Here's how Pryzma answers them.
What model processes our data?
Pryzma uses a proprietary reasoning engine for threat classification and anomaly detection, with Anthropic's Claude integrated for conversational AI capabilities. We disclose our full architecture because transparency is a security posture, not a liability.
Does our data train your model?
No. Customer data is never used to train any model — ours or any third party's. Our models are trained exclusively on de-identified Safe Harbor data. Your operational data stays in your governed environment.
Where does our data go?
We provide a complete data flow diagram showing every system, API, and service that touches your data. No black boxes. No undisclosed third-party API calls. Full auditability from ingestion to insight.
Can you produce a BAA chain?
Yes. For healthcare deployments, every layer of the Pryzma stack — from data ingestion to AI inference to storage — is covered by executed Business Associate Agreements. We can produce the full chain on request.
What happens if we need to audit?
Pryzma maintains complete audit logs of every data access, every AI inference, every investigation action, and every system event. Available on demand, exportable in standard formats, retention-configurable to your policy.
Built in production. Not in a pitch deck.
11M+
Patient access events monitored
340+
Organizations tracked
5-tier
Adaptive threat classification
3,936
Mining report pages cited by page
870
Historical mine workings placed in 3D
Full stack
BAA coverage
Scale your team without scaling headcount.
See how Pryzma extends what your people can do — compliance, reporting, integration, investigation — all powered by AI that works alongside them.
Schedule a Demo